Black October: Why Cybersecurity Matters More Than Ever in the AI Age
Nov 12, 2026
/
Tolga Ünlü
Table of Contents
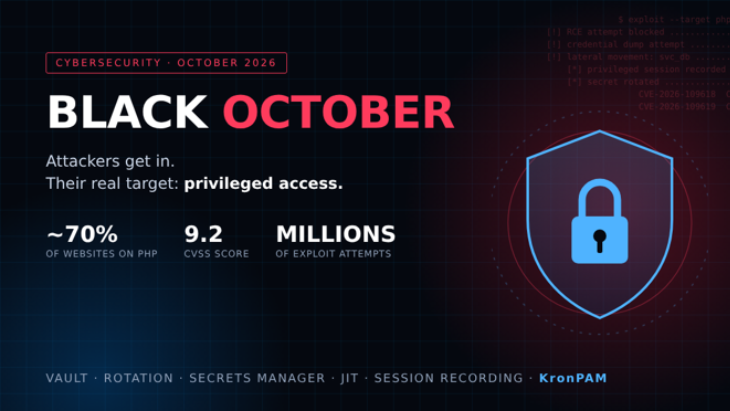
October 2026 is being called "Black October" after two critical PHP vulnerabilities triggered a global wave of attacks. From Europe to Japan, public institutions and financial firms had to temporarily suspend services.
The lesson is clear: in the age of AI, vulnerabilities are found and exploited faster than most organizations can defend. Cybersecurity is no longer an IT cost; it is a guarantee of business continuity and reputation.
What happened in Black October?
Two critical PHP flaws (CVE-2026-109618 and CVE-2026-109619, CVSS 9.2) can, under certain conditions, let attackers run code on a server without authentication. Roughly 70% of websites use PHP. That does not mean 70% of sites were attacked, but it shows how wide the attack surface is.
|
Date |
Event |
|
22 Oct |
Exploit attempts reached the millions; measures began across Asia |
|
21 Oct |
PHP released fixed versions (8.2.35, 8.3.36, 8.4.27, 8.5.12) one day ahead of schedule |
|
20 Oct |
Details of the flaws leaked online |
|
24 Aug |
Wiz reported a second flaw, found with AI assistance |
|
11 Aug |
The first critical flaw, found through AI-assisted research, was reported to PHP developers |
According to Cloudflare CEO Matthew Prince, exploit attempts climbed to tens of thousands within 45 minutes of disclosure, hundreds of thousands within 2 hours, and then millions.
Global impact:
- Europe: In the Netherlands, the Overheid.nl portal, the Port of Rotterdam and some hospitals; public services in France, Germany, Belgium, Finland and Denmark were temporarily taken offline. UK councils including Oxford and Edinburgh saw outages.
- Asia: In Japan, financial firms including Mitsubishi UFJ Financial Group suspended some online services. South Korea raised its cyber alert level; China advised organizations to renew accounts and access keys.
- Türkiye: The Cyber Security Presidency issued a national warning and launched preventive measures.
Most shutdowns were precautionary; there is no verified count of successful breaches yet.
Three lessons from Black October
- AI has multiplied the speed of vulnerability discovery. Former CISA director Chris Krebs noted that about 3% of all critical vulnerabilities ever discovered were found in the past month. Patching and detection capacity is not keeping pace.
- The real goal is to move inside. Once on a web server, attackers first look for database passwords, service accounts and API keys in configuration files. The vulnerability opens the door; privileged credentials open the whole building.
- "Rotate all access keys" is easier said than done. Without central credential management, it means weeks of manual work and new outage risk.
Why PAM is decisive: limiting the damage with KronPAM
Patches close today's vulnerability. Privileged Access Management (PAM) limits the damage of the one that will be discovered tomorrow. KronPAM makes every step an attacker needs after the initial breach harder:
|
Attacker's step |
Kron PAM capability |
Outcome |
|
Steal passwords and API keys from config files |
Passwords, keys and tokens embedded in applications are managed centrally; no static secrets remain on a compromised server |
|
|
Use stolen credentials |
Password vault and automatic rotation |
Critical account passwords are rotated regularly, and organization-wide in one click during an incident |
|
Escalate privileges and move laterally |
Just-in-Time access and least privilege |
Standing privileges disappear; access is granted only when needed and for a limited time |
|
Act on critical systems without a trace |
Session monitoring and recording |
Every privileged action is visible, auditable and available for post-incident review |
|
Blend in as a normal user |
Anomalous behavior is detected; critical access requires additional verification |
For an organization running KronPAM, China's advice to "renew accounts and access keys" is not a weeks-long project; it is a central rotation policy.
Checklist for organizations
- Inventory every system running PHP and update to the fixed versions
- Restrict external access to, or temporarily disable, systems that cannot be updated
- Look for signs of compromise on systems running older versions
- Find every password and key embedded in applications and config files and bring them under central management
- Rotate privileged and service account passwords
- Review standing admin rights and move to JIT access
- Enforce MFA and session recording for access to critical systems
Conclusion
Black October showed that cybersecurity is more valuable than ever and is now a boardroom issue. No one knows when the next critical vulnerability will surface. Organizations that keep privileged access under control can turn that day's crisis into a manageable incident.
To assess your organization's privileged access risks together, get in touch with the Kron team.